Nishi Family › Compare › Containers and Orchestration
Nishi Compare · capabilities, evidence and delivery
Containers and Orchestration
Compare capabilities and delivery evidence. Source discovery, qualification, deployment and accepted outcomes are separate; an open contract names work still to verify.
The sovereign daemonless Nishi Container Host vs Docker Desktop and Portainer and Podman and Kubernetes -- runtime measured live on the RTX 5080 Windows host that runs Elder AI image-gen off Docker
Overview
The purpose, declared position and evidence coverage of this domain. Source presence and completed acceptance are different measures.
Where we are. The sovereign daemonless container host is real and measured on the RTX 5080 host: Windows Job-Object isolation and lifecycle, a declarative ContainerSpec driving a 2560-byte governance PE, a topological compose planner, live supervision with self-restart, never-brick deploy, one-command ship, fleet inventory API and SSE, the Sovereign Fleet UI, native GPU ownership (10.9GB VRAM image-gen live), rootless zero-admin operation, and a content-addressed registry. Four measured exceeds: 0 MB idle, 2560-byte runtime, 976 ms cold start with zero VM tax, whole runtime auditable bits-up. Named gaps: quota depth, syscall filtering, P2P distribution.
Where we need to go. Isolation the Linux stack takes for granted -- bounded cpu, memory and io per governed child and a syscall filter -- without giving up the zero-overhead exceeds, and distribution of container PEs peer-to-peer over the live torrent plane by digest.
Research bar. Docker and the OCI stack is measured on seccomp default profiles, cgroups quotas, Hub plus OCI distribution. Theirs: the Linux isolation and distribution reference. Ours: CT1 CT2 CT3 measured on this page.
Research bar. Kubernetes is measured on requests and limits per container, liveness probes. Theirs: the orchestration reference. Ours: CT1.
Latest recorded release
No valid dated release entry is recorded for this domain.
Release entries describe recorded changes; they do not establish that every capability passed evaluation.
15 of 22 capability source symbols found|1 of them authored stronger-claims|7 open|coverage 681/1000|adoption 6 full / 9 partial
Evidence profile — what the gaps on this board actually are
Measured by nx_swcompare_evidence, read back by nx_evprofile_lib. Every figure is a count with its denominator — there is deliberately no score, no grade and no percentage anywhere in this band, because a stored scalar is a field a seat can edit and a counted partition is not.
evidence|grounded 19/19|unsupported 0|gates green 1/1|proven able to fail 1/1|never bitten 0|green at 0/0 0|open gaps 3|of them unnamed 0|of them proof withheld 0|flips ready 0
proven able to fail counts the gates that have a RECORDED RED — nx_gate_bite mutated the gate subject, rebuilt it, watched the gate go red, and that record is inside the shared TTL. never bitten is its complement over the same denominator: those gates ran and were green, and nothing has ever shown them able to detect anything, so their green is a statement about this run and not about the gate. green at 0/0 is a separate and much weaker observation — the gate printed GREEN on a zero denominator, so its own tooth counter says it examined nothing. A gate can be green, non-zero, and still never bitten; that is the common case and it is now visible instead of implied.
partition: grounded + unsupported = 19 vs present 19 · named + unnamed + withheld = 3 vs open 3 · both reconcile
liar-kill conj=GPQN · all four conjuncts held
graded document: BUILDROOT tree, 10644 bytes · gates map: PRIMARY · stamped 1d 7h ago · source ../knowledge/status/evstamp_containers.verdict
| Gap class | What it is, and the work it names |
|---|---|
| NONE | No gap class fires on this board: every published claim is grounded, the declared gates ran and were green, no watch contract is unnamed or already landed, and the stamp is inside its TTL. That is a statement about evidence, not about depth, scale or polish. |
nx_swcompare_evidence containers itself and are not carried on the stamp, so this page names the classes and the producer names the rows. That split is stated rather than hidden: a count without a worklist is not actionable, and this band is honest about which half of that it is.Production map
Follow the dependencies, declared acceptance criteria and recorded priorities. Inspect source binding before treating a rank as executable work.
Ranking source binding: STALE_INCONSISTENT. Recorded priorities require current acceptance evidence and resource checks before execution.
Recorded ranking withheld
Retained ranking is not bound to the current plan and matrix: STALE_INCONSISTENT. Historical data remains retained. Refresh the ranking after resolving the input differences. Latest execution outcome is unverified.
Declared roadmap — contract, acceptance, executor, effort
| Rung | Closes with | Definition of done (pre-declared) | Executor | Est. |
|---|---|---|---|---|
| Job-Object governance (CT0) | SetInformationJobObject | Basic Job limits live on the governed child -- LANDED | Organ | 0 u |
| Content-addressed registry (CR0) | CONTAINERREGISTRYGATE | Put and get by digest, tampered blob refused -- LANDED gated | Organ | 0 u |
| Quota depth (CT1) after CT0 | pe_job_quota_set | cpu-rate, working-set and io quotas read from the ContainerSpec and applied to the Job before CreateProcessW; gate proves a child that exceeds its working-set quota is BOUNDED (page-faulted, not killed) and a spec without quotas is refused by the emitter | Organ | 1.5 u |
| Syscall filter (CT2) after CT0 | sc_syscall_filter | A per-spec deny-list enforced on the governed child through the host's native mitigation policy surface; gate proves a denied call in the child fails with the policy named while the same binary outside the filter succeeds (the positive control) | Organ | 3 u |
| P2P publish by digest (CT3) after CR0 | reg_p2p_publish | Publish a registry blob onto the live torrent plane keyed by its SHA-256; gate proves a second host pulls it peer-to-peer and the digest verifies, and a corrupted piece is refused by the same check | Organ | 1.5 u |
Milestones
| Milestone | Rungs | Cumulative |
|---|---|---|
| M1 · Bounded children | CT1 | 1.5 u |
| M2 · Distributed by digest | CT3 | 3 u |
| M3 · Filtered like the Linux stack | CT2 | 6 u |
| Rung | Closes with | Definition of done (pre-declared) | Executor | Est. |
|---|---|---|---|---|
| Reference tools run on demand with complete owned lifecycle (CT4) after CT1,CR0 | _ABSENT_:oracle_tool_journey_accept | SOURCE-BOUND PLANNING CONTRACT 2026-09-24. Compose nx_container, the content-addressed registry and existing job/host resource owners. A versioned reference-tool definition names dependency/license identities, admitted host resources, inputs, expected evidence and owner. One callable workflow prepares and invokes the reference outside the sovereign build path, retains complete outputs and exact identity, and releases processes/resources on success, failure, cancellation and abandoned-run recovery. Prove ready reuse, cold preparation, missing dependency UNAVAILABLE, denied resource admission, nonzero child, cancellation and cleanup using an actual representative existing viewer/rigger. No permanent background load is required for an on-demand reference; no model provider is contacted. Human interpretation of reference results remains distinct from a successful container run. Effort unestimated. | Workflow | unestimated u |
| Class | Count | Note |
|---|---|---|
| bars | 0 | sotabar rows on the plan |
| fresh | 0 | the bar month is the current month |
| attested | 0 | an older bar with a this-month barscan reporting no newer entry |
| stale | 0 | a this-month scan saw a newer month the bar ignores |
| unattested | 0 | nobody looked this month |
| malformed | 0 | a sotabar row missing a field |
| duplicate | 0 | bar ids an earlier row already carries |
| bars, summed | 0 | RECONCILED: the parts sum to the total 0 |
| current month | 2026-10 | the month every bar is judged against |
Inspect a rung and its prerequisites
Declared nodes 6. Rank input binding: STALE_INCONSISTENT. Dependency order is authored. Implementation, acceptance evidence, authority and resource readiness are unverified. No action is recommended or dispatched here.
Plan SHA-256 5268e050f905d34b18d192147bafd376142b3a25b81885774b4da62ed151b605. Target rows 0; role rows 0. Existing risks and release worklog retain their own scope; no node completion is inferred.
Runtime observation coverage: 0 of 6 rungs have current, identity-bound execution observations. Observation may report RED. Accepted completion remains unknown; source presence, qualification and deployment do not establish it.
Use Enter or Space on a rung to inspect its contract. Prerequisite links locate another rung in this list; open its summary to inspect it. Estimates are authored effort, not forecasts.
CT0 — Job-Object governance
Prerequisites: None declared; this does not establish execution eligibility.
Contract:
SetInformationJobObjectAcceptance: Basic Job limits live on the governed child -- LANDED
Authored effort: 0. Executor kind: Organ. Responsible, accountable and verifier not established. Inspect retained worklog.
Runtime observation: UNKNOWN; outcome UNKNOWN; observed epoch -1. Declared owner: . Receipt
, SHA-256. Identity-bound observation is not accepted completion. Qualification and deployment remain unverified by this projection.CR0 — Content-addressed registry
Prerequisites: None declared; this does not establish execution eligibility.
Contract:
CONTAINERREGISTRYGATEAcceptance: Put and get by digest, tampered blob refused -- LANDED gated
Authored effort: 0. Executor kind: Organ. Responsible, accountable and verifier not established. Inspect retained worklog.
Runtime observation: UNKNOWN; outcome UNKNOWN; observed epoch -1. Declared owner: . Receipt
, SHA-256. Identity-bound observation is not accepted completion. Qualification and deployment remain unverified by this projection.CT1 — Quota depth
Prerequisites: CT0 (acceptance unverified)
Contract:
pe_job_quota_setAcceptance: cpu-rate, working-set and io quotas read from the ContainerSpec and applied to the Job before CreateProcessW; gate proves a child that exceeds its working-set quota is BOUNDED (page-faulted, not killed) and a spec without quotas is refused by the emitter
Authored effort: 1.5. Executor kind: Organ. Responsible, accountable and verifier not established. Inspect retained worklog.
Runtime observation: UNKNOWN; outcome UNKNOWN; observed epoch -1. Declared owner: . Receipt
, SHA-256. Identity-bound observation is not accepted completion. Qualification and deployment remain unverified by this projection.CT2 — Syscall filter
Prerequisites: CT0 (acceptance unverified)
Contract:
sc_syscall_filterAcceptance: A per-spec deny-list enforced on the governed child through the host's native mitigation policy surface; gate proves a denied call in the child fails with the policy named while the same binary outside the filter succeeds (the positive control)
Authored effort: 3. Executor kind: Organ. Responsible, accountable and verifier not established. Inspect retained worklog.
Runtime observation: UNKNOWN; outcome UNKNOWN; observed epoch -1. Declared owner: . Receipt
, SHA-256. Identity-bound observation is not accepted completion. Qualification and deployment remain unverified by this projection.CT3 — P2P publish by digest
Prerequisites: CR0 (acceptance unverified)
Contract:
reg_p2p_publishAcceptance: Publish a registry blob onto the live torrent plane keyed by its SHA-256; gate proves a second host pulls it peer-to-peer and the digest verifies, and a corrupted piece is refused by the same check
Authored effort: 1.5. Executor kind: Organ. Responsible, accountable and verifier not established. Inspect retained worklog.
Runtime observation: UNKNOWN; outcome UNKNOWN; observed epoch -1. Declared owner: . Receipt
, SHA-256. Identity-bound observation is not accepted completion. Qualification and deployment remain unverified by this projection.CT4 — Reference tools run on demand with complete owned lifecycle
Prerequisites: CT1 (acceptance unverified), CR0 (acceptance unverified)
Contract:
_ABSENT_:oracle_tool_journey_acceptAcceptance: SOURCE-BOUND PLANNING CONTRACT 2026-09-24. Compose nx_container, the content-addressed registry and existing job/host resource owners. A versioned reference-tool definition names dependency/license identities, admitted host resources, inputs, expected evidence and owner. One callable workflow prepares and invokes the reference outside the sovereign build path, retains complete outputs and exact identity, and releases processes/resources on success, failure, cancellation and abandoned-run recovery. Prove ready reuse, cold preparation, missing dependency UNAVAILABLE, denied resource admission, nonzero child, cancellation and cleanup using an actual representative existing viewer/rigger. No permanent background load is required for an on-demand reference; no model provider is contacted. Human interpretation of reference results remains distinct from a successful container run. Effort unestimated.
Authored effort: unestimated. Executor kind: Workflow. Responsible, accountable and verifier not established. Inspect retained worklog.
Runtime observation: UNKNOWN; outcome UNKNOWN; observed epoch -1. Declared owner: . Receipt
, SHA-256. Identity-bound observation is not accepted completion. Qualification and deployment remain unverified by this projection.
Learning and practice paths
No structured learning path is declared for this plan. Existing research, roadmap and worklog remain available above.
Rung dossiers — every record that bears on a rung, in one place
nx_swcompare_evidence containers writes it beside its stamp); every gate below reads UNRECORDED until it runs.knowledge/organ_gate.conf read from this working directory (1 rows) and from the estate root (196 rows); rows in both counted once: 0; declarations read: 197. Every declaration in either copy counts, so a stub beside the publisher can never hide the root.CT0 Job-Object governance · cell NO-MATRIX-ROW · gate NO-MATRIX-ROW
| Contract | SetInformationJobObject · executor Organ · 0 u · stands on nothing |
|---|---|
| Definition of done | Basic Job limits live on the governed child -- LANDED |
| Matrix cell | NO-MATRIX-ROW — no matrix row carries SetInformationJobObject; the ranker reads this rung as unmapped and no cell can flip for it. Add the row and the join completes on the next publish. |
| Gate | the gate join needs a matrix row: no organ is named for this rung |
| Work log | no log row names this rung yet |
CR0 Content-addressed registry · cell PRESENT · gate NO-GATE-DECLARED
| Contract | CONTAINERREGISTRYGATE · executor Organ · 0 u · stands on nothing |
|---|---|
| Definition of done | Put and get by digest, tampered blob refused -- LANDED gated |
| Matrix cell | Image registry and distribution · runtime/nx_container_registry.nx · PRESENT marker |
| Gate | NO-GATE-DECLARED — knowledge/organ_gate.conf carries no row for nx_container_registry; declare nx_container_registry TAB <gate> and the ship loop proves it and the verdict lands here. |
| Work log | no log row names this rung yet |
CT1 Quota depth · cell WATCHING · gate NO-GATE-DECLARED
| Contract | pe_job_quota_set · executor Organ · 1.5 u · stands on CT0 |
|---|---|
| Definition of done | cpu-rate, working-set and io quotas read from the ContainerSpec and applied to the Job before CreateProcessW; gate proves a child that exceeds its working-set quota is BOUNDED (page-faulted, not killed) and a spec without quotas is refused by the emitter |
| Matrix cell | Resource quota depth (cpu, memory, io bound per governed child) · runtime/nx_pe_container_win.nx · WATCHING decl |
| Gate | NO-GATE-DECLARED — knowledge/organ_gate.conf carries no row for nx_pe_container_win; declare nx_pe_container_win TAB <gate> and the ship loop proves it and the verdict lands here. |
| Work log | no log row names this rung yet |
CT2 Syscall filter · cell WATCHING · gate NO-GATE-DECLARED
| Contract | sc_syscall_filter · executor Organ · 3 u · stands on CT0 |
|---|---|
| Definition of done | A per-spec deny-list enforced on the governed child through the host's native mitigation policy surface; gate proves a denied call in the child fails with the policy named while the same binary outside the filter succeeds (the positive control) |
| Matrix cell | Syscall-filter sandboxing depth · runtime/nx_container_seccomp.nx · WATCHING decl |
| Gate | NO-GATE-DECLARED — knowledge/organ_gate.conf carries no row for nx_container_seccomp; declare nx_container_seccomp TAB <gate> and the ship loop proves it and the verdict lands here. |
| Work log | no log row names this rung yet |
CT3 P2P publish by digest · cell WATCHING · gate NO-GATE-DECLARED
| Contract | reg_p2p_publish · executor Organ · 1.5 u · stands on CR0 |
|---|---|
| Definition of done | Publish a registry blob onto the live torrent plane keyed by its SHA-256; gate proves a second host pulls it peer-to-peer and the digest verifies, and a corrupted piece is refused by the same check |
| Matrix cell | P2P image distribution over the live torrent plane · runtime/nx_container_registry.nx · WATCHING decl |
| Gate | NO-GATE-DECLARED — knowledge/organ_gate.conf carries no row for nx_container_registry; declare nx_container_registry TAB <gate> and the ship loop proves it and the verdict lands here. |
| Work log | no log row names this rung yet |
CT4 Reference tools run on demand with complete owned lifecycle · cell NO-MATRIX-ROW · gate NO-MATRIX-ROW
| Contract | _ABSENT_:oracle_tool_journey_accept · executor Workflow · unestimated u · stands on CT1, CR0 |
|---|---|
| Definition of done | SOURCE-BOUND PLANNING CONTRACT 2026-09-24. Compose nx_container, the content-addressed registry and existing job/host resource owners. A versioned reference-tool definition names dependency/license identities, admitted host resources, inputs, expected evidence and owner. One callable workflow prepares and invokes the reference outside the sovereign build path, retains complete outputs and exact identity, and releases processes/resources on success, failure, cancellation and abandoned-run recovery. Prove ready reuse, cold preparation, missing dependency UNAVAILABLE, denied resource admission, nonzero child, cancellation and cleanup using an actual representative existing viewer/rigger. No permanent background load is required for an on-demand reference; no model provider is contacted. Human interpretation of reference results remains distinct from a successful container run. Effort unestimated. |
| Matrix cell | NO-MATRIX-ROW — no matrix row carries oracle_tool_journey_accept; the ranker reads this rung as unmapped and no cell can flip for it. Add the row and the join completes on the next publish. |
| Gate | the gate join needs a matrix row: no organ is named for this rung |
| Work log | 2026-10-02 queue INTAKE 1790952449 routed by nx_intake_route (codex-root, epoch 1790952847) from codex-root: [resource-management][NAS foundation priority] Operator feedback2026-10-02: "this doesnt seem sota to not proactively manage the resources id like the nishi estate and future nishi os and nishi browse -- sponsor intake-1790952449 plus2 |
dossiers=6 cells_joined=4 no_matrix_row=2 (sum 6) gates_recorded=0 gates_unrecorded=0 no_gate_declared=4 (sum 4 of cells_joined) evgates=UNSTAMPED
Capability comparisons
Compare the field, search individual capabilities and open their source and adoption evidence. Documented presence does not establish comparative quality.
Position map — centrality and distinctiveness
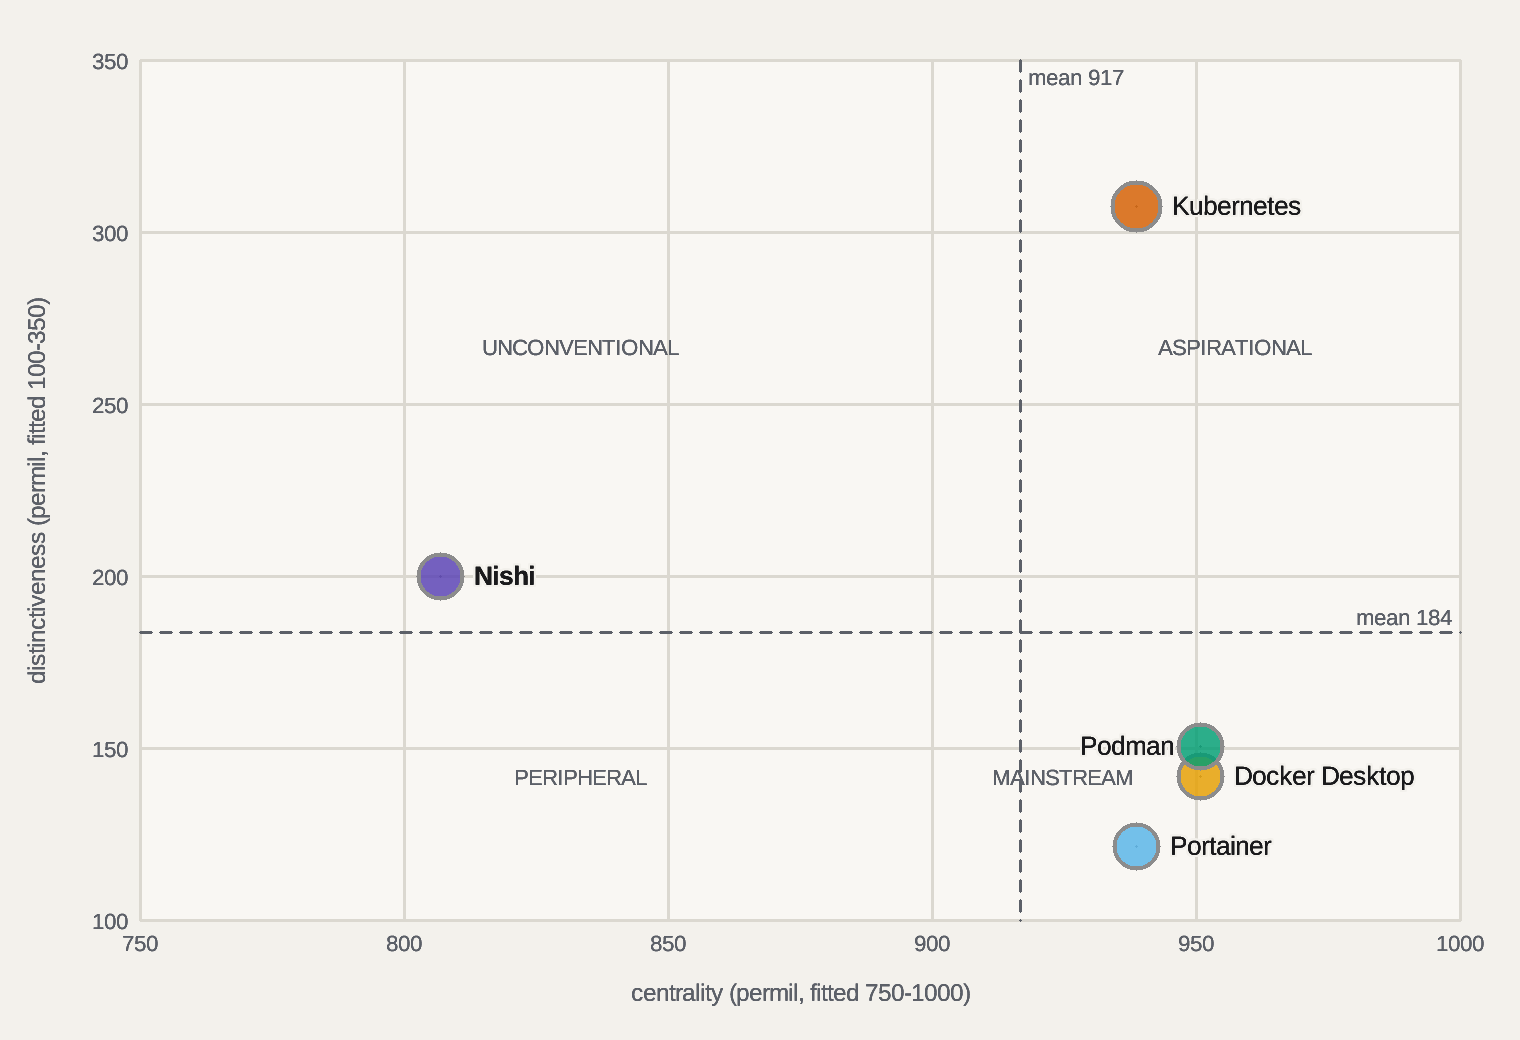
The four-quadrant map the field uses for brand strategy (Dawar and Bagga, HBR June 2015), re-derived from this matrix on every publish. Centrality is the share of the category's feature mass a player covers, each feature weighted by how many hold it; distinctiveness is the average lead over each rival on the rows the player holds; breadth is the depth-weighted share of the whole matrix (the bubble); depth is how deeply the rows held are held; momentum is the day-over-day move off the spine (green rising, red falling, grey until day two); the dashed path runs first day → previous day → today. Dividers are the category means. Axes are fitted to the field of play, so read the tick numerals, not the frame. Rival marks are documented presence, so a rival's position reads the record, never its quality. The picture grades its own readability below; the table beside it is the same data for a screen reader or a second method.
knowledge/compare/containers.cdmap (cut|x|y, cube|x|y|z); absent = the HBR defaultsbubble area = breadth · ring = momentum (green rising, red falling, grey until day two) · dashed = category means · axes fitted to the field of play: centrality 750–1000, distinctiveness 100–350 of 0–1000 permil (the full range put every player in one corner)
readability of the 2D cut, self-graded by the layout ruler: label overlaps 0 · labels over marks 0 · off-canvas 0 · unresolved labels 0 · mark overlaps 1 (a fact of the data: two players that close are that close) · data spread 659 permil of the plot · quadrant words unseated 0
text contrast, measured with wcag2-ratio (floors from contrast.conf), light theme: labels 16.24 (floor 4.50) · notes 16.24 (floor 4.50) · quadrant words 5.89 (floor 4.50) · tick numerals 5.89 (floor 4.50) · axis titles 5.59 (floor 4.50) · dark theme: labels 13.78 (floor 4.50) · quadrant words 5.55 (floor 4.50) · axis titles 5.97 (floor 4.50) · dark classes under their floor 0 (one figure serves both themes: a dark shortfall is a token to fix, never a class to hide) · classes refused under their floor 0 (a refused class is not drawn; the scale classes are measured, never hidden) · export: SVG PNG (receipt, rendered by the estate's own rasteriser from this page)

readability of the 3D cube, self-graded by the layout ruler: label overlaps 0 · labels over marks 0 · off-canvas 2 · unresolved labels 0 · mark overlaps 1 (a fact of the data: two players that close are that close) · data spread 280 permil of the plot
10 panels over 5 registered axes, every pair once (the lower axis on x, the higher on y) · each panel fitted to its own field of play, first and last tick numerals shown · no labels in a small cut, the legend names the colours; the grade below reports the mark terms only (MM summed over the panels, spread averaged)
readability of the small multiples, self-graded by the layout ruler: label overlaps 0 · labels over marks 0 · off-canvas 0 · unresolved labels 0 · mark overlaps 15 (a fact of the data: two players that close are that close) · data spread 521 permil of the plot
| Player | Quadrant | centrality | distinctiveness | breadth | depth | momentum | Rows held | Days on spine | First seen |
|---|---|---|---|---|---|---|---|---|---|
| Nishi | Unconventional | 807 | 200 | 469 | 688 | 0 since 2026-09-23 | 15 | 10 | 2026-09-15 |
| Docker Desktop | Mainstream | 951 | 142 | 500 | 647 | 0 since 2026-09-23 | 17 | 10 | 2026-09-15 |
| Portainer | Mainstream | 939 | 122 | 439 | 568 | 0 since 2026-09-23 | 17 | 10 | 2026-09-15 |
| Podman | Mainstream | 951 | 151 | 500 | 647 | 0 since 2026-09-23 | 17 | 10 | 2026-09-15 |
| Kubernetes | Aspirational | 939 | 308 | 636 | 823 | 0 since 2026-09-23 | 17 | 10 | 2026-09-15 |
| Day | Matrix rows reviewed | Players recorded |
|---|---|---|
| 2026-09-15 | 22 | 5 |
| 2026-09-16 | 22 | 5 |
| 2026-09-17 | 22 | 5 |
| 2026-09-18 | 22 | 5 |
| 2026-09-19 | 22 | 5 |
| 2026-09-20 | 22 | 5 |
| 2026-09-21 | 22 | 5 |
| 2026-09-22 | 22 | 5 |
| 2026-09-23 | 22 | 5 |
| 2026-10-08 | 22 | 5 |
players 5|matrix rows 22|feature mass 83|centrality mean 917|distinctiveness mean 184|axes 5|spine days 10 (shown 10)|rows written today 0|readability defects 2D 0 cube 2|spine knowledge/status/cdmap/containers.spine
Capability matrix — measured against source
◉ authored stronger claim; source present● present◐ partial○ absent? unassessed; excluded from relative comparison · click any capability for its evidence
Peer cell coverage: authored assessed 88, unassessed 0. Authored assessments are not verified outcomes.
No capabilities match this filter or search.
| Capability | Nishi | Docker Desktop | Portainer | Podman | Kubernetes |
|---|---|---|---|---|---|
Process isolation primitiveMeasured:nx_pe_emit_container exists in runtime/nx_pe_container_win.nx, verified at emit. Linux stack isolates via namespaces plus cgroups and K8s pods; Portainer delegates to the engine it manages; Nishi governs natively via Windows Job Objects [win-job-objects]. SYMBOL REPOINTED 2026-09-01: the row cited CreateJobObjectW, which is a WINDOWS API NAME and not a sovereign function, so the one-symbol ruler correctly refused it and the OLD substring ruler had been grounding the row against a COMMENT. THE SAME ROW APPEARS IN THREE BOARDS (containers, swarm, workermesh) AND WAS THE ENTIRE RED FOR ALL THREE -- one cause, three domains, which is why collapsing to causes before sizing a campaign matters. The defining sovereign function in that organ is nx_pe_emit_container. A ROW THAT CITES A FOREIGN OS API HAS NO SOVEREIGN DEFINITION TO GROUND AGAINST -- name the wrapper, never the syscall it wraps Adoption: SOURCE-ONLY — PARTIAL: source exists, never compiled: /api/build it.Pros Implementing source symbol found; runtime acceptance separate; ahead of PortainerCons not adopted yet: source exists, never compiled: /api/build it | ● | ● | ◐ | ● | ● |
Lifecycle governance run-wait-reapMeasured:nx_pe_emit_container exists in runtime/nx_pe_container_win.nx, verified at emit. Nishi container PE creates the Job then CreateProcessW then Wait then ExitCode then clean reap -- proven live governing the CUDA engine. SYMBOL REPOINTED 2026-09-01: the row cited a WINDOWS API NAME, which has no sovereign definition to ground against, so the one-symbol ruler correctly refused it while the OLD substring ruler had been matching it inside a COMMENT. Name the wrapper, never the syscall it wraps. ⚠READ THIS BEFORE COUNTING THIS BOARD AS FOUR CAPABILITIES: nx_pe_container_win.nx defines exactly ONE public function, nx_pe_emit_container, and FOUR axes on this board now ground on it. That is honest (the organ header says it composes the Job boundary plus limit plus CreateProcessW plus Wait plus GetExitCode plus reap in one emitter) but it is THIN EVIDENCE -- four claimed capabilities backed by one symbol are not four independent groundings, and the right fix is to split the emitter so each axis has its own provable surface. Stated rather than hidden, because a row that grounds is not the same as a row that is separately evidenced rival marks uncited — the Yes, Best or Part codes on this row are an observation read with no reference mark behind them Adoption: SOURCE-ONLY — PARTIAL: source exists, never compiled: /api/build it.Pros Implementing source symbol found; runtime acceptance separateCons not adopted yet: source exists, never compiled: /api/build it | ● | ● | ● | ● | ● |
Declarative service specOpen — no implementing organ is measured for this axis yet. K8s declarative YAML is the reference; Compose files yes; Portainer edits stacks over an engine; Nishi ContainerSpec drives the emitter from data rival marks uncited — the Yes, Best or Part codes on this row are an observation read with no reference mark behind themPros none measured yetCons behind Docker Desktop, Portainer, Podman, Kubernetes (leads); no implementing organ measured | ○ | ● | ◐ | ● | ◉ |
Build runnable artifact from specMeasured:CONTAINERSPECGATE exists in runtime/nx_container_spec_emit.nx, verified at emit. docker build with BuildKit is Best in class; podman build yes; K8s delegates builds; Nishi stamps the spec onto a proven 2560-byte governance PE template rival marks uncited — the Yes, Best or Part codes on this row are an observation read with no reference mark behind them Adoption: SOURCE-ONLY — PARTIAL: source exists, never compiled: /api/build it.Pros Implementing source symbol found; runtime acceptance separate; ahead of Portainer, KubernetesCons behind Docker Desktop (leads); not adopted yet: source exists, never compiled: /api/build it | ● | ◉ | ◐ | ● | ○ |
Multi-service orchestration dependency orderMeasured:CONTAINERCOMPOSEGATE exists in runtime/nx_container_compose.nx, verified at emit. K8s is the orchestration reference; compose depends_on yes; podman kube partial; Nishi topological planner rejects cycles and missing deps by construction rival marks uncited — the Yes, Best or Part codes on this row are an observation read with no reference mark behind them Adoption: SOURCE-ONLY — PARTIAL: source exists, never compiled: /api/build it.Pros Implementing source symbol found; runtime acceptance separate; ahead of Portainer, PodmanCons behind Kubernetes (leads); not adopted yet: source exists, never compiled: /api/build it | ● | ● | ◐ | ◐ | ◉ |
Health probe plus auto-restart supervisionMeasured:crash-loop exists in runtime/_hdl_build/nx_hostctl.nx, verified at emit. K8s liveness and readiness probes are Best [k8s-probes]; Docker healthcheck and restart policies; Nishi hostctl supervise runs live in production (PID-liveness plus SERVING probe HUNG-aware plus crash-loop backoff) AND the Windows container PE now self-restarts its governed child -- respawn proven live with 3 distinct child PIDs, hand-emitted in a 2560-byte PE Adoption: PRODUCER-ALIAS — fully adopted (top of its ladder).Pros Implementing source symbol found; runtime acceptance separate; ahead of Podman; fully adopted on the estate ladderCons behind Kubernetes (leads) | ● | ● | ● | ◐ | ◉ |
Never-brick deploy health-gated promote auto-rollbackMeasured:ma_do_deploy exists in runtime/_hdl_build/nx_mgmt_api.nx, verified at emit. K8s rolling update can undo; plain Docker and Podman have none; Portainer redeploys without health-gated auto-rollback; Nishi /api/deploy watchdog rolls back BY CONSTRUCTION rival marks uncited — the Yes, Best or Part codes on this row are an observation read with no reference mark behind them Adoption: LIVE-DAEMON — fully adopted (top of its ladder).Pros Implementing source symbol found; runtime acceptance separate; ahead of Docker Desktop, Portainer, Podman; fully adopted on the estate ladderCons behind Kubernetes (leads) | ● | ○ | ◐ | ○ | ◉ |
One-command source to live pipelineMeasured:SHIPPED exists in runtime/nx_ship.nx, verified at emit. Portainer GitOps stack redeploy is its strength; Nishi nx_ship packs then uploads then builds on target over sovereign TLS in one command rival marks uncited — the Yes, Best or Part codes on this row are an observation read with no reference mark behind them Adoption: RUN-BY:fork:nx_ws_hygiene_gate — fully adopted (top of its ladder).Pros Implementing source symbol found; runtime acceptance separate; ahead of Docker Desktop, Podman, Kubernetes; fully adopted on the estate ladderCons behind Portainer (leads) | ● | ◐ | ◉ | ◐ | ◐ |
Live fleet inventory APIMeasured:/api/services exists in runtime/_hdl_build/nx_mgmt_api.nx, verified at emit. Portainer UI and kubectl get are Best; docker ps yes; Nishi GET /api/services serves the live multi-service inventory over the sovereign mgmt API rival marks uncited — the Yes, Best or Part codes on this row are an observation read with no reference mark behind them Adoption: LIVE-DAEMON — fully adopted (top of its ladder).Pros Implementing source symbol found; runtime acceptance separate; fully adopted on the estate ladderCons behind Portainer (leads), Kubernetes (leads) | ● | ● | ◉ | ● | ◉ |
Event stream monitoring hooksMeasured:event-stream exists in runtime/_hdl_build/nx_mgmt_api.nx, verified at emit. docker events yes; K8s watch API Best; Nishi GET /api/events serves text/event-stream to EventSource clients rival marks uncited — the Yes, Best or Part codes on this row are an observation read with no reference mark behind them Adoption: LIVE-DAEMON — fully adopted (top of its ladder).Pros Implementing source symbol found; runtime acceptance separate; fully adopted on the estate ladderCons behind Kubernetes (leads) | ● | ● | ● | ● | ◉ |
Container fleet management web UIMeasured:ma_emit_dashboard exists in runtime/_hdl_build/nx_mgmt_api.nx, verified at emit. Portainer is the reference container UI but needs a root-equivalent engine socket [portainer-docs]; Nishi Sovereign Fleet at /health is LIVE behind the operator login -- per-service cards with state and crash-loop and port-squatter warnings, allowlisted restart actions, deploy status and an SSE live tick, rendered by the engine itself Adoption: LIVE-DAEMON — fully adopted (top of its ladder).Pros Implementing source symbol found; runtime acceptance separate; ahead of Docker Desktop, Podman; fully adopted on the estate ladderCons behind Portainer (leads), Kubernetes (leads) | ● | ◐ | ◉ | ◐ | ◉ |
GPU workloads in containersMeasured:sd-server exists in runtime/nx_pe_container_sdserver.nx, verified at emit. Docker Desktop routes GPU through the WSL2 VM [docker-desktop-gpu]; podman CDI and K8s device plugins are Linux-native; the Nishi-governed child owns the RTX 5080 natively -- 10.9GB VRAM Z-Image generation proven live Adoption: SOURCE-ONLY — PARTIAL: source exists, never compiled: /api/build it.Pros Implementing source symbol found; runtime acceptance separate; ahead of Docker Desktop, PortainerCons not adopted yet: source exists, never compiled: /api/build it | ● | ◐ | ◐ | ● | ● |
Rootless least-privilege operationMeasured:nx_pe_emit_container exists in runtime/nx_pe_container_win.nx, verified at emit. Podman pioneered rootless and is Best [podman-rootless]; Docker rootless mode is non-default; Portainer needs the engine socket which is root-equivalent; Nishi runs as the plain user with zero daemon and zero admin. SYMBOL REPOINTED 2026-09-01: the row cited a WINDOWS API NAME, which has no sovereign definition to ground against, so the one-symbol ruler correctly refused it while the OLD substring ruler had been matching it inside a COMMENT. Name the wrapper, never the syscall it wraps. ⚠READ THIS BEFORE COUNTING THIS BOARD AS FOUR CAPABILITIES: nx_pe_container_win.nx defines exactly ONE public function, nx_pe_emit_container, and FOUR axes on this board now ground on it. That is honest (the organ header says it composes the Job boundary plus limit plus CreateProcessW plus Wait plus GetExitCode plus reap in one emitter) but it is THIN EVIDENCE -- four claimed capabilities backed by one symbol are not four independent groundings, and the right fix is to split the emitter so each axis has its own provable surface. Stated rather than hidden, because a row that grounds is not the same as a row that is separately evidenced Adoption: SOURCE-ONLY — PARTIAL: source exists, never compiled: /api/build it.Pros Implementing source symbol found; runtime acceptance separate; ahead of Docker Desktop, Portainer, KubernetesCons behind Podman (leads); not adopted yet: source exists, never compiled: /api/build it | ● | ◐ | ○ | ◉ | ◐ |
Resource limit quotasMeasured:nx_pe_emit_container exists in runtime/nx_pe_container_win.nx, verified at emit. cgroups give full cpu-mem-io quotas and K8s requests-limits are Best [linux-namespaces7]; Nishi Job-Object limits are basic today -- quota depth is a named gap. SYMBOL REPOINTED 2026-09-01: the row cited a WINDOWS API NAME, which has no sovereign definition to ground against, so the one-symbol ruler correctly refused it while the OLD substring ruler had been matching it inside a COMMENT. Name the wrapper, never the syscall it wraps. ⚠READ THIS BEFORE COUNTING THIS BOARD AS FOUR CAPABILITIES: nx_pe_container_win.nx defines exactly ONE public function, nx_pe_emit_container, and FOUR axes on this board now ground on it. That is honest (the organ header says it composes the Job boundary plus limit plus CreateProcessW plus Wait plus GetExitCode plus reap in one emitter) but it is THIN EVIDENCE -- four claimed capabilities backed by one symbol are not four independent groundings, and the right fix is to split the emitter so each axis has its own provable surface. Stated rather than hidden, because a row that grounds is not the same as a row that is separately evidenced Adoption: SOURCE-ONLY — PARTIAL: source exists, never compiled: /api/build it.Pros Implementing source symbol found; runtime acceptance separateCons behind Kubernetes (leads); not adopted yet: source exists, never compiled: /api/build it | ● | ● | ● | ● | ◉ |
Syscall-filter sandboxing depthOpen — watchingruntime/nx_container_seccomp.nx : sc_syscall_filter, re-measured on every compare beat. Ship that symbol and this mark flips itself; the comparewatch- plane row flips with it. seccomp and AppArmor ship default on the Linux stack [docker-seccomp] and gVisor or Kata harden further; Nishi has Job-Object boundaries only -- no syscall filter yetPros none measured yetCons behind Docker Desktop, Portainer, Podman, Kubernetes (leads); open contract; expected source declaration not established | ○ | ● | ● | ● | ◉ |
Resource quota depth (cpu, memory, io bound per governed child)DARK —runtime/nx_pe_container_win.nx EXISTS but does not declare pe_job_quota_set: something shipped at this path under another name, and this mark would read open forever. Repoint the contract to the real entry point (the plan rung AND this row) or rename the function; the flip follows on the next beat, and the comparewatch- plane row reads DARK until then. The resource-limit row above is present at BASIC Job-Object depth; cgroups v2 and K8s requests-limits bound cpu, memory and io per container -- the contract is per-spec cpu-rate, working-set and io quotas applied to the Job before the child starts, proven by a child that exceeds its quota being bounded not killed rival marks uncited — the Yes, Best or Part codes on this row are an observation read with no reference mark behind themPros none measured yetCons behind Docker Desktop, Portainer, Podman, Kubernetes (leads); open contract; expected source declaration not established | ○ | ● | ● | ● | ◉ |
P2P image distribution over the live torrent planeDARK —runtime/nx_container_registry.nx EXISTS but does not declare reg_p2p_publish: something shipped at this path under another name, and this mark would read open forever. Repoint the contract to the real entry point (the plan rung AND this row) or rename the function; the flip follows on the next beat, and the comparewatch- plane row reads DARK until then. The content-addressed registry row above is present; Docker Hub plus OCI distribution is the ecosystem reference -- the contract named in that row's own note is publish-by-digest onto the live torrent plane so a second host pulls a container PE peer-to-peer and verifies the same SHA-256 rival marks uncited — the Yes, Best or Part codes on this row are an observation read with no reference mark behind themPros none measured yetCons behind Docker Desktop (leads), Portainer, Podman (leads), Kubernetes; open contract; expected source declaration not established | ○ | ◉ | ◐ | ◉ | ● |
Image registry and distributionMeasured:CONTAINERREGISTRYGATE exists in runtime/nx_container_registry.nx, verified at emit. Docker Hub plus OCI distribution is the ecosystem Best and Podman is full OCI [oci-distribution]; Nishi now has a sovereign content-addressed registry -- put and get by name where the SHA-256 digest IS the address (dedup plus integrity by construction), a tampered blob is refused on pull; proven on real container PEs (byte-identical round-trip), P2P distribution over the live torrent plane is the next rung Adoption: BUILT-UNPROMOTED — PARTIAL: compiled, never promoted to the serving root: /api/promote it.Pros Implementing source symbol found; runtime acceptance separate; ahead of PortainerCons behind Docker Desktop (leads), Podman (leads); not adopted yet: compiled, never promoted to the serving root: /api/promote it | ● | ◉ | ◐ | ◉ | ● |
EXCEED measured: idle overhead 0 MB 0 processesOpen — no implementing organ is measured for this axis yet. Measured live on this host: Nishi 0 MB and 0 procs idle vs Docker Desktop 2774 MB and 6 procs [docker-desktop-docs]; a K8s control plane is heavier still; verdicts computed by the liar-killed judge nx_container_benchPros none measured yetCons no implementing organ measured | ○ | ○ | ○ | ○ | ○ |
EXCEED measured: runtime install 2560 bytesOpen — no implementing organ is measured for this axis yet. The whole Nishi container runtime is a 2560-byte PE vs Docker Desktop 4.11 GB install [docker-desktop-docs]; Portainer adds hundreds of MB on top of an engine it requiresPros none measured yetCons no implementing organ measured | ○ | ○ | ○ | ○ | ○ |
EXCEED measured: cold start 976 ms with zero VM taxOpen — no implementing organ is measured for this axis yet. First governed process 976 ms vs Docker 1660 ms and isolation VM tax 0 vs 2225 MB -- no WSL2 or HyperV VM under the runtime on Windows [docker-desktop-docs]Pros none measured yetCons no implementing organ measured | ○ | ○ | ○ | ○ | ○ |
EXCEED sovereign: whole runtime auditable bits-upSource present; authored stronger claim:Job-governs in runtime/nx_pe_container_sdserver.nx, verified at emit. The entire runtime emitter orchestrator and judge are readable sovereign source with zero third-party dependencies; incumbents are millions of lines over kernel plumbing no operator can audit Adoption: SOURCE-ONLY — PARTIAL: source exists, never compiled: /api/build it.Pros Source symbol found; stronger capability claim is authored; ahead of Docker Desktop, Portainer, Podman, KubernetesCons not adopted yet: source exists, never compiled: /api/build it | ◉ | ○ | ○ | ○ | ○ |
| Class | Count | Note |
|---|---|---|
| rows with rival marks | 18 | rows carrying a Yes, Best or Part in a rival column |
| cited | 8 | a reference mark resolves to a pinned mirror |
| uncited | 10 | an observation read, badged until a reference lands |
| rows, summed | 18 | RECONCILED: the parts sum to the total 18 |
Delivery and evidence
Inspect risks, technical debt, rendered observations, experiments and references. Read scope and limitations alongside every result.
Risk register
| Risk | Likelihood x impact | Mitigation |
|---|---|---|
| A filter that blocks a call the governed CUDA engine needs bricks image-gen, the only production workload | possible x high | CT2 ships with the positive control (the engine's full syscall set recorded first) and never-brick deploy behind it. |
| Quotas that kill instead of bound turn a slow child into an outage | possible x medium | CT1 done-rule is BOUNDED not killed; the kill path stays the supervisor's, single responsibility. |
Release history and work log
| When | Rung | Kind | Entry |
|---|---|---|---|
| 2026-10-02 | CT4 | queue | INTAKE 1790952449 routed by nx_intake_route (codex-root, epoch 1790952847) from codex-root: [resource-management][NAS foundation priority] Operator feedback2026-10-02: "this doesnt seem sota to not proactively manage the resources id like the nishi estate and future nishi os and nishi browse -- sponsor intake-1790952449 plus2 |
Person · product · place — not yet measured for this domain
knowledge/compare/containers.ppp (rows surface|nishi or c1..c4|label|url|connect naming OUR live surface and each rival's front door), run nx_ppp_probe domain containers, and this section fills itself on the next beat: the same ruler on both sides — privacy and CX (third-party hosts, tracker classes, cookies, security headers), design and longevity (design hygiene, computed WCAG contrast, render-blocking resources, unsized media, script weight, theme and motion queries), findability (landmarks, skip link, on-site search, breadcrumb, headings, internal links).The field — discovered, not chosen
Rows written by nx_field_discover from containers.seeds: the industry's own lists (Wikipedia wikitext, GitHub topics, awesome lists) read mechanically, every candidate counted across seeds. The matrix columns above are a SEAT'S pick; this band is the population they were picked from, and the stats line measures one against the other. A rival here is a lead, never a verdict — it earns a column when its capabilities are read and pinned.
| Class | Count | Note |
|---|---|---|
| seeds | 4 | |
| scanned | 4 | |
| fetched | 4 | |
| reused | 0 | |
| failed | 0 | |
| named | 4 | |
| candidates | 4 | |
| mentions | 4 | |
| capped | 0 |
| Rank | Rival | Seeds | Mentions | First seed | Kind | Link |
|---|---|---|---|---|---|---|
| 1 | Docker Desktop | 1 | 1 | col0-docker | named | https://docs.docker.com/desktop/ |
| 2 | Portainer | 1 | 1 | col1-portainer | named | https://docs.portainer.io/ |
| 3 | Podman | 1 | 1 | col2-podman | named | https://github.com/containers/podman/blob/main/docs/tutorials/rootless_tutorial.md |
| 4 | Kubernetes | 1 | 1 | col3-kubernetes | named | https://kubernetes.io/docs/tasks/configure-pod-container/configure-liveness-readiness-startup-probes/ |
field candidates 4|shown 4 of 4|matrix columns in the field 4 of 4|discovered rivals with no column 0|malformed rows 0 (counted, never rendered)|read-capped 0
Exclusive and shared capabilities
This board grades 19 capabilities: 10 exclusive to it and 9 shared with other boards. Shared rows on this page: 9 = home here 1 + home elsewhere 0 + ambiguous 0 + undecided 8 + refused 0 (partition 9); undecided = unmapped 0 + unproven 8 + unevidenced 0; homonyms 0; since the previous census: new 0, resolved 0. Census FRESH age_s=6458.
| Capability | Organ | Boards grading it | Home | Rule | Evidence | Standing on this board |
|---|---|---|---|---|---|---|
| event-stream | nx_mgmt_api.nx | automation, deploy, containers | — | none | unproven | undecided |
| ma_do_deploy | nx_mgmt_api.nx | cms, containers | — | none | unproven | undecided |
| SHIPPED | nx_ship.nx | deploy, containers | — | none | unproven | undecided |
| crash-loop | nx_hostctl.nx | deploy, containers | — | none | unproven | undecided |
| /api/services | nx_mgmt_api.nx | deploy, containers | — | none | unproven | undecided |
| ma_emit_dashboard | nx_mgmt_api.nx | deploy, containers | — | none | unproven | undecided |
| nx_pe_emit_container | nx_pe_container_win.nx | swarm, workermesh, containers | — | none | unproven | undecided |
| CONTAINERREGISTRYGATE | nx_container_registry.nx | swarm, workermesh, containers* | containers | rung | plan | home here |
| sd-server | nx_pe_container_sdserver.nx | workermesh, containers | — | none | unproven | undecided |
Gaps from the record — what the estate does that no board carries
The record census (nx_goalmap record) reads the invoked-tool population and every plan queue row and files each organ or directive that NO matrix, plan or gates row names. A row here is a callout the boards missed: adjudicate it onto a board or declare it infrastructure. Census state STALE (age 1395563 s), sources read 4 of 7 declared — a BLIND census is a FLOOR: unread sources can only add rows.
| kind | name | board | source | evidence |
|---|
rows shown 0|this board's directives 0|estate-wide un-boarded organs 452 (listed in full on /compare/ecosystem)|census rows 639|malformed 0 (counted, never rendered)
References
- [docker-desktop-docs] Docker Inc. Docker Desktop documentation (docs.docker.com/desktop): the Windows/macOS/Linux desktop product that bundles Docker Engine, CLI, Compose and BuildKit inside a managed VM (WSL 2 or Hyper-V backend on Windows). publisher · read in our library
knowledge/fetched/cmp_containers_docker-desktop.html· pinh5302a649aeea9618d7da96a9736c3651f6369d50dbc6edef137ac1feb90a5f6e· accessed 2026-08-18 · vendor-docGrounds: The Docker Desktop column across the register and the three EXCEED measured rows -- idle overhead 0 MB 0 processes, runtime install 2560 bytes, cold start 976 ms with zero VM tax: the 2774 MB / 6 processes / 4.11 GB / 1660 ms incumbent numbers were measured against THIS product on the same host, and its VM-backed architecture is why the isolation VM tax exists at all. - [docker-desktop-gpu] Docker Inc. GPU support in Docker Desktop (docs.docker.com/desktop/features/gpu): NVIDIA GPU access from containers on Windows via the WSL 2 backend and the NVIDIA driver for WSL. publisher · read in our library
knowledge/fetched/cmp_containers_docker-gpu.html· pinhd4164e8141f3e08200e516f740df49d6369666007febe2bcaed660cdf9c9bdaf· accessed 2026-08-18 · vendor-docGrounds: The GPU workloads in containers row: Docker Desktop routes the GPU through the WSL 2 VM (Part), which is the exact contrast to the Nishi-governed child owning the RTX 5080 natively -- 10.9 GB VRAM Z-Image generation proven live. - [portainer-docs] Portainer.io. Portainer documentation (docs.portainer.io): container management UI for Docker, Docker Swarm, Kubernetes and Podman environments, deployed as a container connected to the engine socket or agent. publisher · read in our library
knowledge/fetched/cmp_containers_portainer.html· pinh2b67056e20dc9563da7d28906b877cab158d740f023b9a08271d38047088d046· accessed 2026-08-18 · vendor-docGrounds: The Portainer column: Container fleet management web UI (Best, but needs a root-equivalent engine socket), Live fleet inventory API (Best), One-command source to live pipeline (GitOps stack redeploy) and the Process isolation primitive note that Portainer delegates to the engine it manages. - [podman-rootless] Containers project. Basic Setup and Use of Podman in a Rootless environment (docs/tutorials/rootless_tutorial.md in the podman repository): user namespaces, subuid/subgid, no daemon and no root required. publisher · read in our library
knowledge/fetched/cmp_containers_podman-rootless.html· pinhc872c5bc6a95bd22216ac3c31eb42499bb459054d0d5cbced8da503d042ef094· accessed 2026-08-18 · vendor-docGrounds: The Rootless least-privilege operation row where Podman is Best (pioneered rootless, daemonless) -- the bar the Nishi plain-user zero-daemon zero-admin PE is graded against -- and the Podman column on Build runnable artifact and Image registry and distribution (full OCI). - [k8s-probes] The Kubernetes Authors. Configure Liveness, Readiness and Startup Probes (kubernetes.io/docs/tasks/configure-pod-container). publisher · read in our library
knowledge/fetched/cmp_containers_k8s-probes.html· pinh2c91059571135379613836c808ab83040714818126088e3dd3b200f5accd1c93· accessed 2026-08-18 · vendor-docGrounds: The Health probe plus auto-restart supervision row where K8s liveness and readiness probes are Best: the probe semantics (kubelet restarts a container that fails its liveness probe) are the bar hostctl supervise (PID-liveness plus SERVING probe HUNG-aware plus crash-loop backoff) and the self-restarting Windows container PE are measured against. - [oci-distribution] Open Container Initiative. OCI Distribution Specification (opencontainers/distribution-spec): the HTTP API for pushing and pulling content-addressed blobs and manifests by digest. publisher · read in our library
knowledge/fetched/cmp_containers_oci-distribution.html· pinh542d8e9ad33361f0277a813b4bef0fd7f0db878a173c36f8a75807163c14c6d1· accessed 2026-08-18 · published-standardGrounds: The Image registry and distribution row: Docker Hub plus OCI distribution is the ecosystem Best and Podman is full OCI; the Nishi sovereign registry where the SHA-256 digest IS the address (dedup plus integrity by construction, tampered blob refused on pull) is a content-addressed store of the same shape without the ecosystem. - [win-job-objects] Microsoft. Job Objects (Windows App Development, learn.microsoft.com/windows/win32/procthread/job-objects): a job object allows groups of processes to be managed as a unit with enforceable limits and kill-on-close semantics. publisher · read in our library
knowledge/fetched/cmp_containers_win-job-objects.html· pinh82d0a4ab5248257c09dcced343ed87b5a729448e9d5f7ca13008592294942279· accessed 2026-08-18 · vendor-docGrounds: The Process isolation primitive (CreateJobObjectW), Lifecycle governance run-wait-reap and Resource limit quotas (SetInformationJobObject) rows: the Windows kernel primitive the 2560-byte Nishi container PE governs with, and why quota depth is a named gap versus cgroups. - [linux-namespaces7] Linux man-pages project. namespaces(7) -- overview of Linux namespaces (man7.org): the kernel isolation facility that, with cgroups, underlies Docker, Podman and Kubernetes pods. publisher · read in our library
knowledge/fetched/cmp_containers_namespaces7.html· pinh7b8c94b7eeeb7a07dc063ecfb852959cbe32f01b7d4e33fe90eee9d4d4c1fdc0· accessed 2026-08-18 · vendor-docGrounds: The Process isolation primitive row note that the Linux stack isolates via namespaces plus cgroups and K8s pods, and the Resource limit quotas row where cgroups give full cpu-mem-io quotas -- the Linux-native primitive set the Windows Job-Object lane is contrasted with. - [docker-seccomp] Docker Inc. Seccomp security profiles for Docker (docs.docker.com/engine/security/seccomp): the default seccomp profile shipped with Docker Engine blocks a set of syscalls for every container. publisher · read in our library
knowledge/fetched/cmp_containers_docker-seccomp.html· pinh98a4ffbab2d0856e58a4faa6c335b02b288bec61e2290c8fdbdabeac288c2b08· accessed 2026-08-18 · vendor-docGrounds: The Syscall-filter sandboxing depth row (_ABSENT_ nx_container_seccomp): seccomp ships default on the Linux stack, which is the bar the Job-Object-only Nishi boundary is honestly marked 0 against -- gVisor and Kata harden further and are not cited here.
generated by nx_swcompare_matrix (sovereign NishiLang organ) from knowledge/compare/containers.matrix · source checks show implementation presence; runtime and user-outcome evidence are reported separately · JavaScript supports page controls